Berlin Senate employee executed a command that a website politely asked him to execute.
-
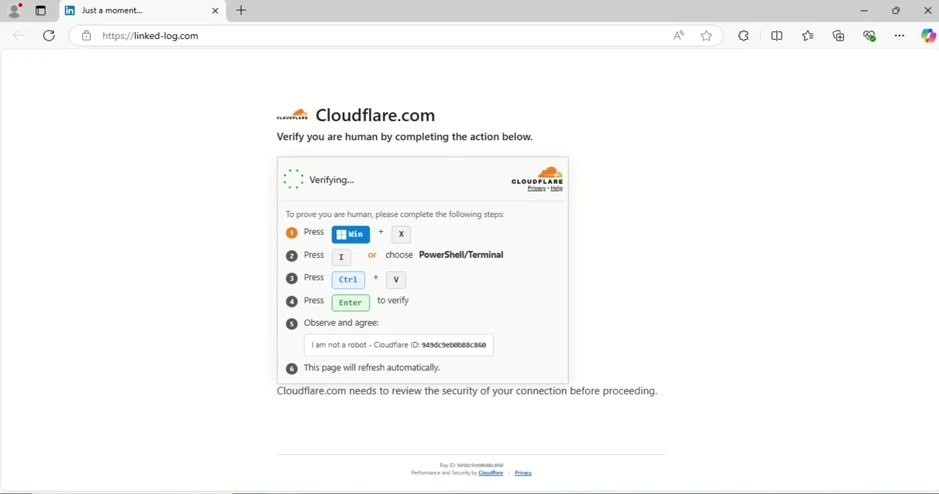
Berlin Senate employee executed a command that a website politely asked him to execute. The page looked like a “verify you are human” check. It instructed to open Windows Terminal/PowerShell, paste a command and press Enter. This is what appears to lead catastrophic results. Attackers hacked the systems and exfiltrated 1.44 million, 5.8 TB. Including personnel records, applications, internal documents, emergency plans and other sensitive material.
-
Berlin Senate employee executed a command that a website politely asked him to execute. The page looked like a “verify you are human” check. It instructed to open Windows Terminal/PowerShell, paste a command and press Enter. This is what appears to lead catastrophic results. Attackers hacked the systems and exfiltrated 1.44 million, 5.8 TB. Including personnel records, applications, internal documents, emergency plans and other sensitive material.
@LukaszOlejnik I understand not every computer user figures out what terminal is. But it's organization's fault they:
- Allow regular users to access terminal;
- Has no rate limiting and observability whatsoever to allow this large exfiltration to happen.
Gross mismanagement

-
Berlin Senate employee executed a command that a website politely asked him to execute. The page looked like a “verify you are human” check. It instructed to open Windows Terminal/PowerShell, paste a command and press Enter. This is what appears to lead catastrophic results. Attackers hacked the systems and exfiltrated 1.44 million, 5.8 TB. Including personnel records, applications, internal documents, emergency plans and other sensitive material.
@LukaszOlejnik Teaching people that it's normal to have to click on unintended things to be able to see the intended thing wasn't very smart.
*) cookie popup
*) are you human popup
*) this website isn't secure popup -
Berlin Senate employee executed a command that a website politely asked him to execute. The page looked like a “verify you are human” check. It instructed to open Windows Terminal/PowerShell, paste a command and press Enter. This is what appears to lead catastrophic results. Attackers hacked the systems and exfiltrated 1.44 million, 5.8 TB. Including personnel records, applications, internal documents, emergency plans and other sensitive material.
@LukaszOlejnik Not something that anyone has ever paid me to configure, but I suspect that disabling PowerShell for regular AD users is really not made to be the easy default that it likely should be.
-
@LukaszOlejnik Teaching people that it's normal to have to click on unintended things to be able to see the intended thing wasn't very smart.
*) cookie popup
*) are you human popup
*) this website isn't secure popup@troed @LukaszOlejnik there’s a term for the growing blasé attitude that develops from having to do this constantly however - “approval fatigue”. This leads to ‘rubber stamping’ where a user will just do the task of clicking or in this case Ctrl-C/Ctrl-V and not expect anything to happen.
macOS is borderline insane with this now: an example is you have to approve an app to read a directory, and it’s per-directory. Secure perhaps but my goodness it’s bloody annoying and exhausting. -
@LukaszOlejnik Not something that anyone has ever paid me to configure, but I suspect that disabling PowerShell for regular AD users is really not made to be the easy default that it likely should be.
@dandels @LukaszOlejnik At least one can stop some things by enforcing constrained language mode. Not sure it would have helped with that payload, though.
-
@LukaszOlejnik Not something that anyone has ever paid me to configure, but I suspect that disabling PowerShell for regular AD users is really not made to be the easy default that it likely should be.
@dandels @LukaszOlejnik My workaround is to disable Win+R (which has an unfortunate side-effect of not allowing you to type a folder name to Explorer's address bar) and to remove PowerShell/Terminal/Command Prompt links from Win+X menu.
-
 A anderslund@expressional.social shared this topic