Happy #ICANN Reveal Fresh Hell Day!
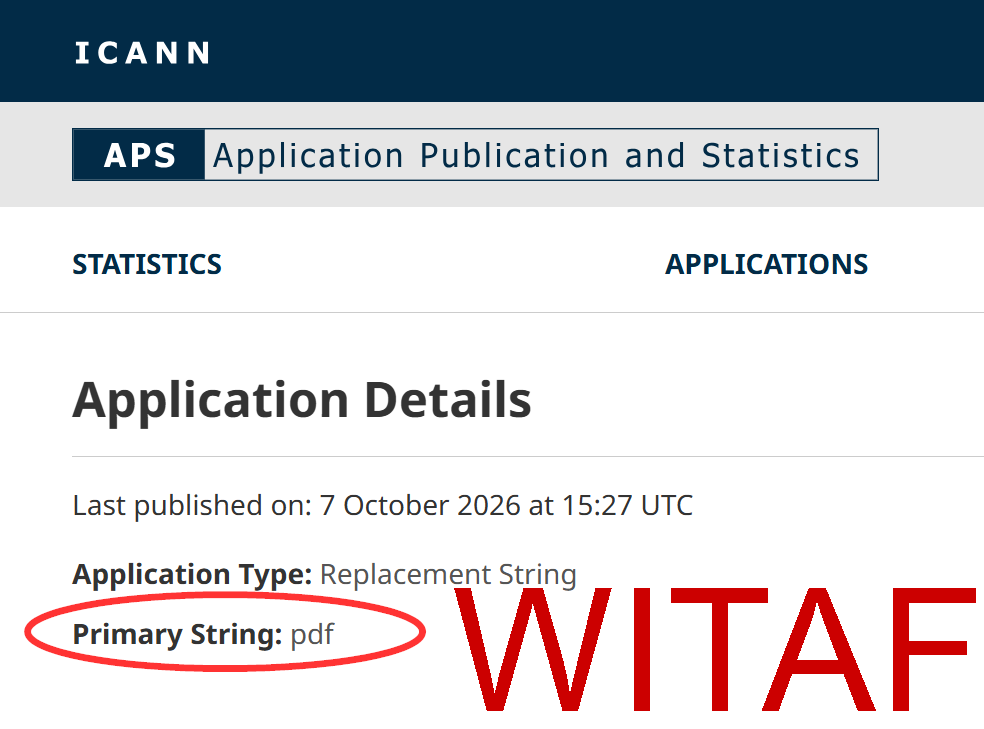
-
@badsamurai so… https://pdf.pdf/pdf.pdf could be a legit url

This is not a new thing.
https://md.md/md.md has been valid for decades.
https://readme.md is run by some AI slop directory.
-
This is not a new thing.
https://md.md/md.md has been valid for decades.
https://readme.md is run by some AI slop directory.
@svavar @badsamurai yeah, but pdf is way funnier than md
-
This is not a new thing.
https://md.md/md.md has been valid for decades.
https://readme.md is run by some AI slop directory.
Correct,
.mdis a ccTLD that's been around longer than markdown. But this is 2026 and these domains have an extremely high likelihood for abuse in phishing, clickfix, and supply chain attacks. ICANN allowing these would be irresponsible.Once these are approved, there will be no oversight.
.duowas applied for by ShortDot, a notorious bulletproof operator known for some of the most abused TLDs on the internet today:.bond.sbs.icuand.cyou -
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai not gonna lie, I kinda hope this one passes
Also the amount of numbered companies in this list is fucking staggering
-
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai
.alder
.bruder -
@badsamurai not gonna lie, I kinda hope this one passes
Also the amount of numbered companies in this list is fucking staggering
@Mustardfacial I am not at all worried typo squatting on
.fartAnd some solid future fedi server TLDs!
.furry.meow.uwu.slay.neko
-
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai the IETF could do something very funny right now: publish an RFC that preemptively reserves the abusable ones.
-
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai oh come tf on

-
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpnRFC 8369 would fix DNS, just saying
-
@mttaggart But no one was really paying attention when CRR (Google) acquired
.zipand .movin 2013.This round we're going to file those objections (string confusion).
No filenames, no intranet names, no assumed trust names.
So I hope these orgs enjoyed their $227,000 donation to ICANN.
https://newgtlds.icann.org/en/program-status/odr#objection-dispute-resolution
I did want someone to get .gif and .jpg so when someone comments "thatsthejoke.gif" or "surprisedpikachu.jpg" it could point to the appropriate one. Kind of like a URI for commonly used memes. It's definitely worth the security issues.
-
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai if submissions of this kind are likely to be rejected, it seems the red teamer's approach is simple -- pick pre-existing TLDs, and introduce them as file extensions for important file types!
Let's invent a new kind of .ai file, or a .net file (a file that connects you to the internet, maybe?)
(Of course, if you're a reasonable human being, this all is actually a terrible idea)
-
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai I'd imagine Adobe would definitely object to this, as well as PHP also objecting to
.php -
@badsamurai if submissions of this kind are likely to be rejected, it seems the red teamer's approach is simple -- pick pre-existing TLDs, and introduce them as file extensions for important file types!
Let's invent a new kind of .ai file, or a .net file (a file that connects you to the internet, maybe?)
(Of course, if you're a reasonable human being, this all is actually a terrible idea)
.com used to be for DOS executables.
https://command.com/ is a home hardware company.
Not sure why this is a problem now all of a sudden.
-
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai kinda like
.zipis being blocked by many corporate firewalls. -
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpnI missed
.lan,.corpand.mailwere also submitted. Corp and mail were originally rejected by ICANN in 2012 as thought too dangerous. Somehow 2026 is safer?.pdfand.phpare technically backup choices, but still an absurd submissions. As is.csrand.bin.The inherent trust words have their own issues:
.login.auth.account.admin.official.verified. I don't see how these are anything but a ransom against organizations to preempt squatting. -
I missed
.lan,.corpand.mailwere also submitted. Corp and mail were originally rejected by ICANN in 2012 as thought too dangerous. Somehow 2026 is safer?.pdfand.phpare technically backup choices, but still an absurd submissions. As is.csrand.bin.The inherent trust words have their own issues:
.login.auth.account.admin.official.verified. I don't see how these are anything but a ransom against organizations to preempt squatting.@badsamurai see i WOULDA said these would be fantastic redteaming domains, but since ai kinda killed redteaming, its now just prompt fodder for various prompt injection attacks and phishing shits
-
@badsamurai the IETF could do something very funny right now: publish an RFC that preemptively reserves the abusable ones.
@gsuberland @badsamurai yes, like
.exampleor.localare… -
.com used to be for DOS executables.
https://command.com/ is a home hardware company.
Not sure why this is a problem now all of a sudden.
@svavar @riverpunk @badsamurai how many #MSDOS machines were on the internet when it was relevant?
- Tinkerers like @rasteri are not the norm and shouldn't be taken as normative example!
-
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai i still can't believe they allowed .zip and .app -
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai Namespace Ian Malcom has some choice words about why they are called ICANN not ISHOULD.