Happy #ICANN Reveal Fresh Hell Day!
-
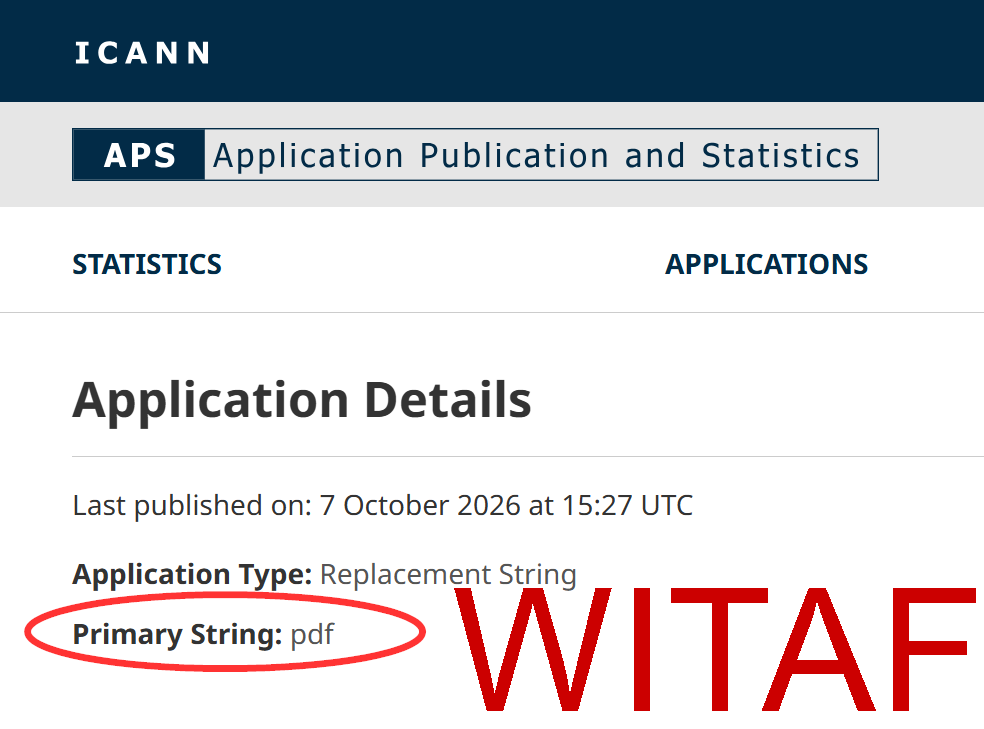
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai Namespace Ian Malcom has some choice words about why they are called ICANN not ISHOULD.
-
@badsamurai see i WOULDA said these would be fantastic redteaming domains, but since ai kinda killed redteaming, its now just prompt fodder for various prompt injection attacks and phishing shits
@Viss @badsamurai exactly!
-
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpnThe applicant list in case y’all want in on the
 and find something I’ve missed.
-
@rl_dane @badsamurai it’s almost like there’s nobody at ICANN who has even vaguely considered the past few decades of cybersecurity
-
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai@infosec.exchange just need .exe now
-
@rl_dane @badsamurai it’s almost like there’s nobody at ICANN who has even vaguely considered the past few decades of cybersecurity
@darkuncle @rl_dane Wait until the infosec
$vendorsstay mum through the entire process. Stopping pre-crime doesn’t exactly increase shareholder value. -
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai No! No god no! Zip was already bad enough what the hell?
-
@darkuncle @rl_dane Wait until the infosec
$vendorsstay mum through the entire process. Stopping pre-crime doesn’t exactly increase shareholder value.@badsamurai @rl_dane there’s a lot more money to be made in selling a mitigation, than in a problem not existing in the first place
-
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpnI have applied for .invalid and .404
-
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai I can accept every single one of them, but .php. There is no reason to use .php but to scam people. Nobody wants to have a domain name associated directly with php, other than php itself probably.
-
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai
At this point, let's just create .exe as a honeypot and mark as phishing any domain that uses it? -
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai
How long before ".corn" is a thing? -
Happy #ICANN Reveal Fresh Hell Day! A company in the Caymans would like the TLD
.pdfAnd these other spectacular submissions that surely won't end poorly:
.sys.key.duo.lab.private.state.auth.conf.config.loc.log.php.url.vpn@badsamurai We already have DNS servers that blanket ban "unsafe" TLDs. Are we asking for even more trouble?
If you run an org/corp, how could you not ban .pdf or .official? -
@badsamurai We already have DNS servers that blanket ban "unsafe" TLDs. Are we asking for even more trouble?
If you run an org/corp, how could you not ban .pdf or .official?@Albi Oh def, I already blocked
.gramon principle. The problem is when they target your customers, partners and supply chains outside of your network. This is commonly observed with recruiting related domains like {brand}jobs and {brand}careers. The domains remain parked, but they’ll have active MX records and never send to your org specifically.Then your average user or small business doesn’t have the skill or tooling to configure firewalls, NextDNS, etc. I take security by design to not just be memory safe computing, but holistic prevention at conceptual birth.
-
@badsamurai see i WOULDA said these would be fantastic redteaming domains, but since ai kinda killed redteaming, its now just prompt fodder for various prompt injection attacks and phishing shits
@Viss @badsamurai is ".wtf" a TLD yet?
-
@Albi Oh def, I already blocked
.gramon principle. The problem is when they target your customers, partners and supply chains outside of your network. This is commonly observed with recruiting related domains like {brand}jobs and {brand}careers. The domains remain parked, but they’ll have active MX records and never send to your org specifically.Then your average user or small business doesn’t have the skill or tooling to configure firewalls, NextDNS, etc. I take security by design to not just be memory safe computing, but holistic prevention at conceptual birth.
@badsamurai I already advocate for taking down/replacing/avoiding the current domain name system due to it's architecture constraints, control and censorship concerns and lack of ownership.
From what I know the only viable alternative is namecoin, which I am not too fond of and still disagree with the way it works fundamentally.
We need an alternative URI for an alternative DNS revolution, not just a patch on the current infrastructure.
When we mix 2 DNS authorities together, we get problems. -
@Viss @badsamurai is ".wtf" a TLD yet?
@ai6yr @Viss @badsamurai It could be!

-
@Viss @badsamurai is ".wtf" a TLD yet?
-
@himysyed @ai6yr @badsamurai i own a couple .wtf domains

-
@Viss @badsamurai is ".wtf" a TLD yet?
@ai6yr @Viss @badsamurai my go to IP checker is https://myip.wtf/