Skip to content
  • Hjem
  • Seneste
  • Etiketter
  • Populære
  • Verden
  • Bruger
  • Grupper
Temaer
  • Light
  • Brite
  • Cerulean
  • Cosmo
  • Flatly
  • Journal
  • Litera
  • Lumen
  • Lux
  • Materia
  • Minty
  • Morph
  • Pulse
  • Sandstone
  • Simplex
  • Sketchy
  • Spacelab
  • United
  • Yeti
  • Zephyr
  • Dark
  • Cyborg
  • Darkly
  • Quartz
  • Slate
  • Solar
  • Superhero
  • Vapor

  • Default (No Skin)
  • No Skin
Kollaps
FARVEL BIG TECH
  1. Forside
  2. Ikke-kategoriseret
  3. Berlin Senate employee executed a command that a website politely asked him to execute.
Berlin Senate employee executed a command that a website politely asked him to execute.

Planlagt Fastgjort Låst Flyttet Ikke-kategoriseret
7 Indlæg 7 Posters 3 Visninger
  • Ældste til nyeste
  • Nyeste til ældste
  • Most Votes
Svar
  • Svar som emne
Login for at svare
Denne tråd er blevet slettet. Kun brugere med emne behandlings privilegier kan se den.
  • lukaszolejnik@mastodon.socialL This user is from outside of this forum
    lukaszolejnik@mastodon.socialL This user is from outside of this forum
    lukaszolejnik@mastodon.social
    wrote sidst redigeret af
    #1

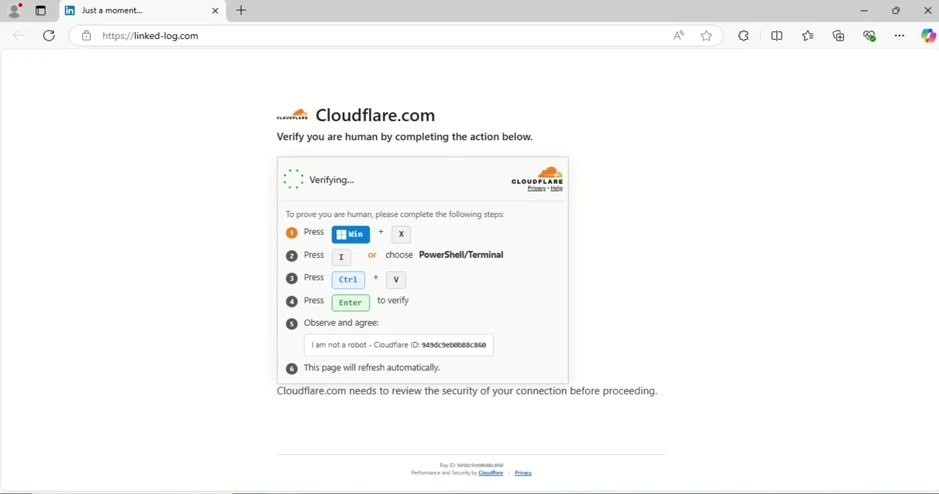
    Berlin Senate employee executed a command that a website politely asked him to execute. The page looked like a “verify you are human” check. It instructed to open Windows Terminal/PowerShell, paste a command and press Enter. This is what appears to lead catastrophic results. Attackers hacked the systems and exfiltrated 1.44 million, 5.8 TB. Including personnel records, applications, internal documents, emergency plans and other sensitive material.

    gytisrepecka@social.gyt.isG troed@swecyb.comT dandels@infosec.exchangeD 3 Replies Last reply
    1
    0
    • lukaszolejnik@mastodon.socialL lukaszolejnik@mastodon.social

      Berlin Senate employee executed a command that a website politely asked him to execute. The page looked like a “verify you are human” check. It instructed to open Windows Terminal/PowerShell, paste a command and press Enter. This is what appears to lead catastrophic results. Attackers hacked the systems and exfiltrated 1.44 million, 5.8 TB. Including personnel records, applications, internal documents, emergency plans and other sensitive material.

      gytisrepecka@social.gyt.isG This user is from outside of this forum
      gytisrepecka@social.gyt.isG This user is from outside of this forum
      gytisrepecka@social.gyt.is
      wrote sidst redigeret af
      #2

      @LukaszOlejnik I understand not every computer user figures out what terminal is. But it's organization's fault they:

      • Allow regular users to access terminal;
      • Has no rate limiting and observability whatsoever to allow this large exfiltration to happen.

      Gross mismanagement

      1 Reply Last reply
      0
      • lukaszolejnik@mastodon.socialL lukaszolejnik@mastodon.social

        Berlin Senate employee executed a command that a website politely asked him to execute. The page looked like a “verify you are human” check. It instructed to open Windows Terminal/PowerShell, paste a command and press Enter. This is what appears to lead catastrophic results. Attackers hacked the systems and exfiltrated 1.44 million, 5.8 TB. Including personnel records, applications, internal documents, emergency plans and other sensitive material.

        troed@swecyb.comT This user is from outside of this forum
        troed@swecyb.comT This user is from outside of this forum
        troed@swecyb.com
        wrote sidst redigeret af
        #3

        @LukaszOlejnik Teaching people that it's normal to have to click on unintended things to be able to see the intended thing wasn't very smart.

        *) cookie popup
        *) are you human popup
        *) this website isn't secure popup

        richrockster@mastodon.socialR 1 Reply Last reply
        0
        • lukaszolejnik@mastodon.socialL lukaszolejnik@mastodon.social

          Berlin Senate employee executed a command that a website politely asked him to execute. The page looked like a “verify you are human” check. It instructed to open Windows Terminal/PowerShell, paste a command and press Enter. This is what appears to lead catastrophic results. Attackers hacked the systems and exfiltrated 1.44 million, 5.8 TB. Including personnel records, applications, internal documents, emergency plans and other sensitive material.

          dandels@infosec.exchangeD This user is from outside of this forum
          dandels@infosec.exchangeD This user is from outside of this forum
          dandels@infosec.exchange
          wrote sidst redigeret af
          #4

          @LukaszOlejnik Not something that anyone has ever paid me to configure, but I suspect that disabling PowerShell for regular AD users is really not made to be the easy default that it likely should be.

          schrotthaufen@mastodon.socialS jernej__s@infosec.exchangeJ 2 Replies Last reply
          0
          • troed@swecyb.comT troed@swecyb.com

            @LukaszOlejnik Teaching people that it's normal to have to click on unintended things to be able to see the intended thing wasn't very smart.

            *) cookie popup
            *) are you human popup
            *) this website isn't secure popup

            richrockster@mastodon.socialR This user is from outside of this forum
            richrockster@mastodon.socialR This user is from outside of this forum
            richrockster@mastodon.social
            wrote sidst redigeret af
            #5

            @troed @LukaszOlejnik there’s a term for the growing blasé attitude that develops from having to do this constantly however - “approval fatigue”. This leads to ‘rubber stamping’ where a user will just do the task of clicking or in this case Ctrl-C/Ctrl-V and not expect anything to happen.
            macOS is borderline insane with this now: an example is you have to approve an app to read a directory, and it’s per-directory. Secure perhaps but my goodness it’s bloody annoying and exhausting.

            1 Reply Last reply
            0
            • dandels@infosec.exchangeD dandels@infosec.exchange

              @LukaszOlejnik Not something that anyone has ever paid me to configure, but I suspect that disabling PowerShell for regular AD users is really not made to be the easy default that it likely should be.

              schrotthaufen@mastodon.socialS This user is from outside of this forum
              schrotthaufen@mastodon.socialS This user is from outside of this forum
              schrotthaufen@mastodon.social
              wrote sidst redigeret af
              #6

              @dandels @LukaszOlejnik At least one can stop some things by enforcing constrained language mode. Not sure it would have helped with that payload, though.

              1 Reply Last reply
              0
              • dandels@infosec.exchangeD dandels@infosec.exchange

                @LukaszOlejnik Not something that anyone has ever paid me to configure, but I suspect that disabling PowerShell for regular AD users is really not made to be the easy default that it likely should be.

                jernej__s@infosec.exchangeJ This user is from outside of this forum
                jernej__s@infosec.exchangeJ This user is from outside of this forum
                jernej__s@infosec.exchange
                wrote sidst redigeret af
                #7

                @dandels @LukaszOlejnik My workaround is to disable Win+R (which has an unfortunate side-effect of not allowing you to type a folder name to Explorer's address bar) and to remove PowerShell/Terminal/Command Prompt links from Win+X menu.

                1 Reply Last reply
                0
                • anderslund@expressional.socialA anderslund@expressional.social shared this topic
                Svar
                • Svar som emne
                Login for at svare
                • Ældste til nyeste
                • Nyeste til ældste
                • Most Votes


                • Log ind

                • Login or register to search.
                Powered by NodeBB Contributors
                Graciously hosted by data.coop
                • First post
                  Last post
                0
                • Hjem
                • Seneste
                • Etiketter
                • Populære
                • Verden
                • Bruger
                • Grupper